ShinyHunters Bypasses Oracle PeopleSoft Firewall Rules
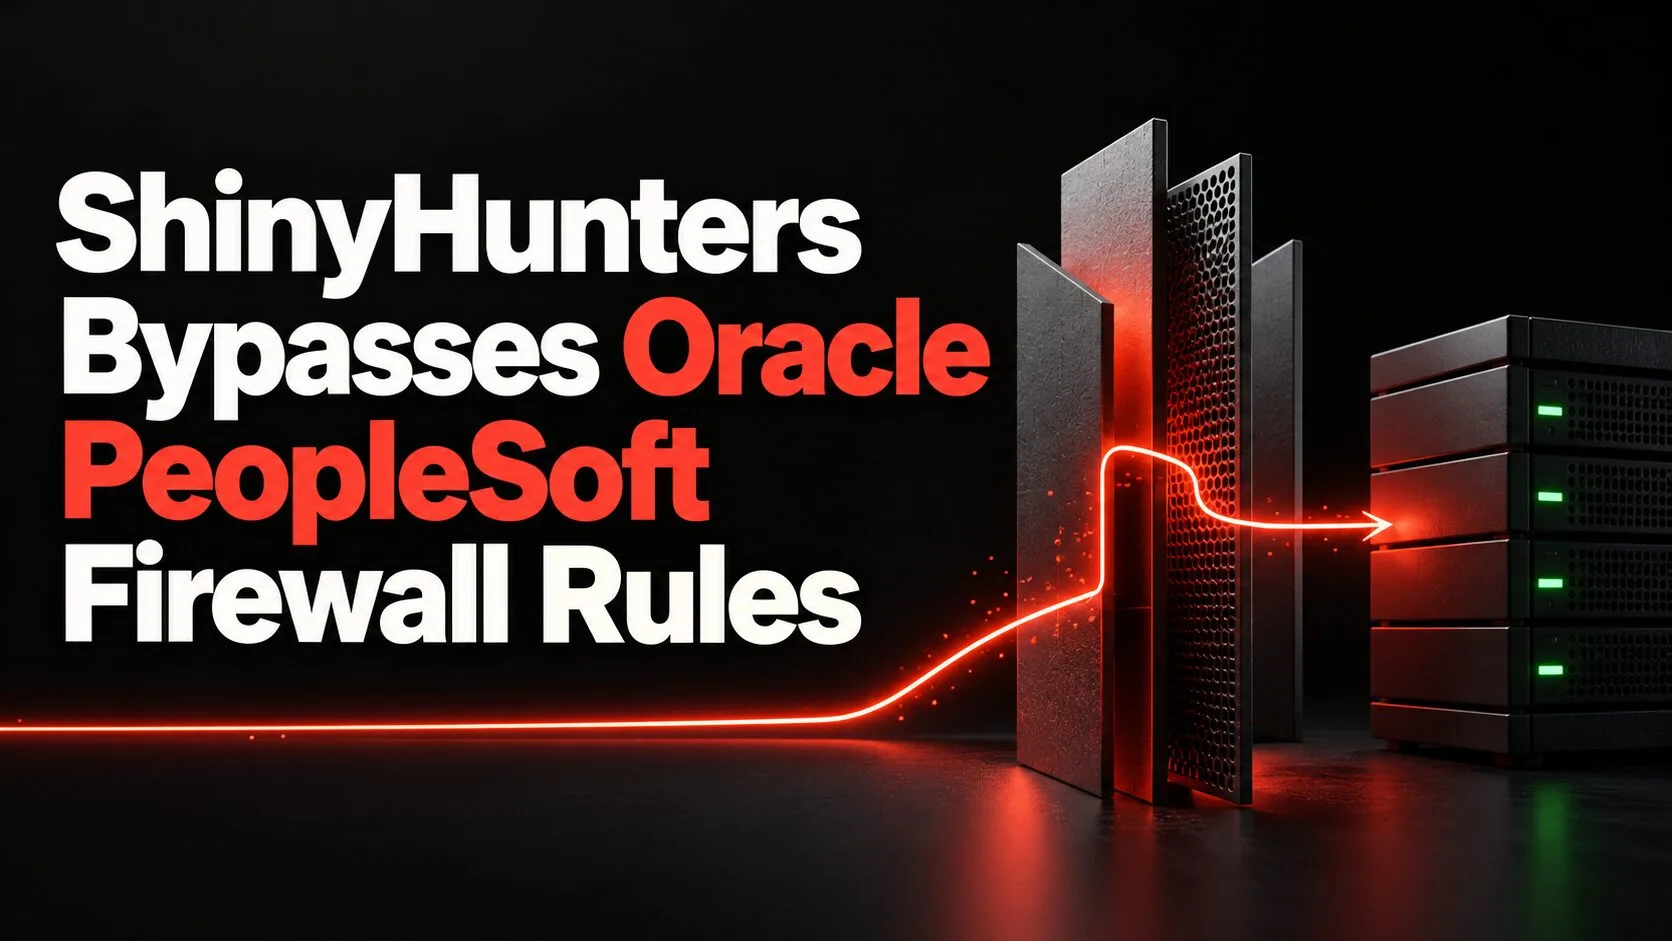
ShinyHunters bypassed Oracle PeopleSoft firewall rules by changing one character in an attack path, Google’s Mandiant unit said on September 25. The updated exploit has placed web shells on dozens of systems across higher education, technology, healthcare, transportation, government and other sectors.
The renewed campaign establishes four urgent facts:
- CVE-2026-35273 is being mass-exploited again.
- The flaw allows unauthenticated remote code execution.
- Literal path-blocking rules can be bypassed.
- Oracle’s security patch remains the primary defense.
ShinyHunters Bypasses Oracle PeopleSoft Firewall Rules
Google Threat Intelligence Group tracks the attackers as UNC6240, a cluster associated with the ShinyHunters name. Its latest report says the group expanded beyond the universities targeted during the original May-to-June campaign and reached organizations in at least seven sectors worldwide.
The vulnerability sits in PeopleSoft Enterprise PeopleTools’ Environment Management Hub, known as EMHub or PSEMHUB. Oracle says CVE-2026-35273 can be exploited remotely without a username or password and may give an attacker the ability to execute code on the affected server.
Oracle assigned the flaw a CVSS score of 9.8 and lists PeopleTools versions 8.61 and 8.62 as affected. The company issued an out-of-band security alert on June 10, after Mandiant observed ShinyHunters exploiting the bug as a zero-day from May 27 through June 9.
How the Encoded PSEMHUB Path Evades WAF Filters
The new attack succeeds against some organizations that installed web application firewall rules but did not patch PeopleSoft. Instead of requesting the blocked /PSEMHUB/ path, the attackers substitute the encoded value %50 for the letter P and send traffic to /%50SEMHUB/.
Some firewalls compare a request with their blocking rule before decoding the path, so the altered string does not match. The PeopleSoft application server then decodes the URL, reconstructs the original PSEMHUB path and forwards the request to the vulnerable servlet.
Mandiant observed five to 15 POST requests arriving before exploitation. Those requests quietly checked whether a server was vulnerable by asking it to return its operating system, allowing the attackers to confirm a target without immediately writing files or disrupting the service.
Related Research
SIDEEYE and Web Shells Extend Access
After gaining entry, the attackers used two exploitation methods. One placed small JSP web shells inside the PeopleSoft application directory; the other executed commands without writing a file, which means monitoring limited to newly created JSP files can miss part of the campaign.
One web shell provided command execution on both Windows and Linux. A second accepted files in 150-kilobyte chunks, helping the attackers assemble larger payloads while avoiding request-size limits. Repeated uploads also helped place shells on multiple nodes behind a load balancer.
On Windows systems, the group deployed a 5.2-megabyte file called Ple64.exe. Mandiant says it masqueraded as a legitimately signed media-player installer but contained a multi-stage backdoor named SIDEEYE. Google contacted certificate issuer Sectigo to seek revocation of the signing certificate.
SIDEEYE can steal browser and desktop credentials, manage files and processes, open an interactive reverse shell and proxy network traffic. Mandiant also found Neo-reGeorg tunneling tools and the legitimate MeshAgent remote-management utility, which can provide persistent interactive access after the initial compromise.
A quarter of the commands Mandiant observed ran as root or NT Authority\SYSTEM, giving the intruders full control of the operating system. Other commands used PeopleSoft or WebLogic service accounts that may still expose application data, database connection strings and other credentials.
Oracle CVE-2026-35273 Patching Is the Priority
Google’s clearest recommendation is to install Oracle’s CVE-2026-35273 security update. WAF filtering and path blocking can reduce exposure, but the one-character bypass demonstrates why those controls are not substitutes for removing the vulnerable code path.
Organizations should also disable EMHub in multi-server configurations when it is not required, or remove the PSEMHUB application in single-server environments. Google says those administrative components can be removed from public internet access without breaking standard PeopleSoft web sessions.
Incident responders should search logs for PSEMHUB requests and encoded variants, inspect application directories for unexpected JSP, JSPX and executable files, and investigate shell processes launched by WebLogic. Systems with a web shell should be treated as compromised rather than merely patched and returned to service.
That response includes preserving evidence and rotating every credential accessible from the PeopleSoft tier. The renewed campaign’s lesson is narrow but important: an emergency perimeter rule may buy time, yet only patching and a full compromise assessment address an adversary already adapting to public defensive guidance.